TL;DR: Between October 20 and November 7, the independent scanner ModGrade flagged malware in dozens of Minecraft projects on CurseForge and Modrinth, including at least seven server plugins. The worst: a CurseForge plugin called LagFixer (anti lag and anti grief) that let an outsider run commands on the machine, and a Modrinth plugin called Mace Smp whose older release downloaded and ran code from an address imitating bStats. Most flagged projects are now removed, but jars already sitting in plugins/ folders keep working. Separately, ModGrade found 12 fake launcher sites copying the Minecraft Launcher, Prism Launcher and HMCL that secretly install ScreenConnect remote access on Windows.
- 7+Server plugins flagged since Oct 20
- 12Fake launcher sites found Nov 5
- 34Projects with malware still online on Oct 27
- 1 dayFake LagFixer stayed up after being found
What happened
ModGrade, an independent scanner that checks CurseForge and Modrinth uploads (it is not affiliated with Mojang or either platform), has been publishing malware finds almost daily since late October. On October 27 it reported malware in 34 projects that were still online at the time, plus six Modrinth mods that carried a hidden download installing a password-stealing browser extension. Since then the finds have kept coming, and a noticeable share are server plugins, not client mods. That changes who is at risk: not one player’s PC, but a whole server and every machine it shares.
One important clarification before you panic: the malicious LagFixer (anti lag and anti grief) was a separate CurseForge upload by the_gang3. It is not the well-known LagFixer by lajczi on Modrinth, Hangar and BuiltByBit, which ModGrade has not flagged. Copying the name of a popular plugin is exactly how these uploads get downloads.
The plugins that were caught
- LagFixer (anti lag and anti grief) by the_gang3, CurseForge. Found November 3, removed November 4. ModGrade says it lets a stranger run commands on your computer or server. File
lagfixer-1.0.jar, built for Bukkit 1.7.2 to 1.15, and confirmed by a human reviewer. - Mace Smp by Luxon, Modrinth. Removed November 7. One of its five files, an older release for Paper, Spigot, Bukkit and Purpur 1.21 to 1.21.11, downloads and runs code from an address that imitates bStats, the metrics service almost every plugin uses.
- Vaults (Breiwalker) and StaffModeration (KervsDev), Modrinth. Same fake-bStats trick, removed around October 25.
- SCF [Slime Chunk Finder], DelexeHub, Bedwars Minigame and AntiFreeCam, CurseForge. Each downloads and runs hidden code. All removed October 24.
Notice the pattern: these are exactly the plugins a small SMP or a new minigame server grabs in a hurry. Anti-lag, anti-cheat, staff tools, a Bedwars mode, a mace SMP. None of them needed to be popular. They only needed to be searched for.
How the fake bStats trick works
Almost every Bukkit and Paper plugin ships a small bStats class that reports anonymous stats to bstats.org. Server owners see that traffic all the time and never question it. The infected plugins bundle what looks like the same metrics code, but it calls home to a look-alike address and pulls down a second program to run. On a server host that means the attacker gets whatever the server process can reach: other plugins’ configs, database passwords, RCON, and sometimes the rest of the box.
Player mods were hit too
- Full Bright (CurseForge) stole Discord tokens and Minecraft sessions. The mod itself was removed October 24, but ModGrade still lists the CurseForge modpack Ultimate Hypixel Package 1.8.9, which bundles it, as online.
- MoreArmor/Weapons (CurseForge) stole saved browser passwords and took screenshots. Removed October 24.
- SimpleTotemCounter (Modrinth) had its malware file removed November 2. CommandCookies Electronic Mod (Modrinth) was still listed as online by ModGrade at the time of writing.
If those names sound like the WeedHack wave all over again, that is because the playbook is the same. Our WeedHack and LofyStealer explainer covers how stolen sessions and Discord tokens get used.
12 fake launcher sites
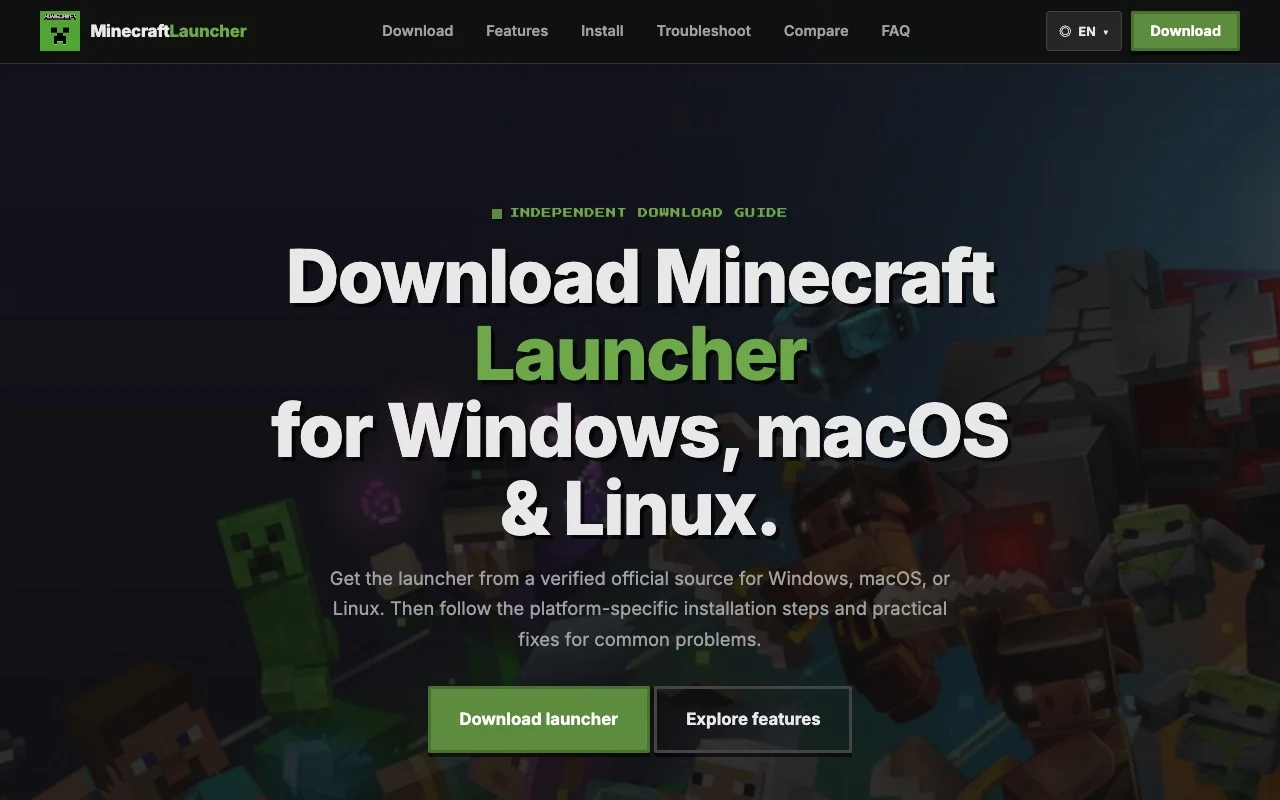
On November 5 ModGrade published its biggest find of the month: twelve websites pretending to be the official Minecraft Launcher, Prism Launcher and HMCL. They reached people the same way the fake cheat-client sites did, through search: some sat on the first page for “hmcl” and “prism launcher”.
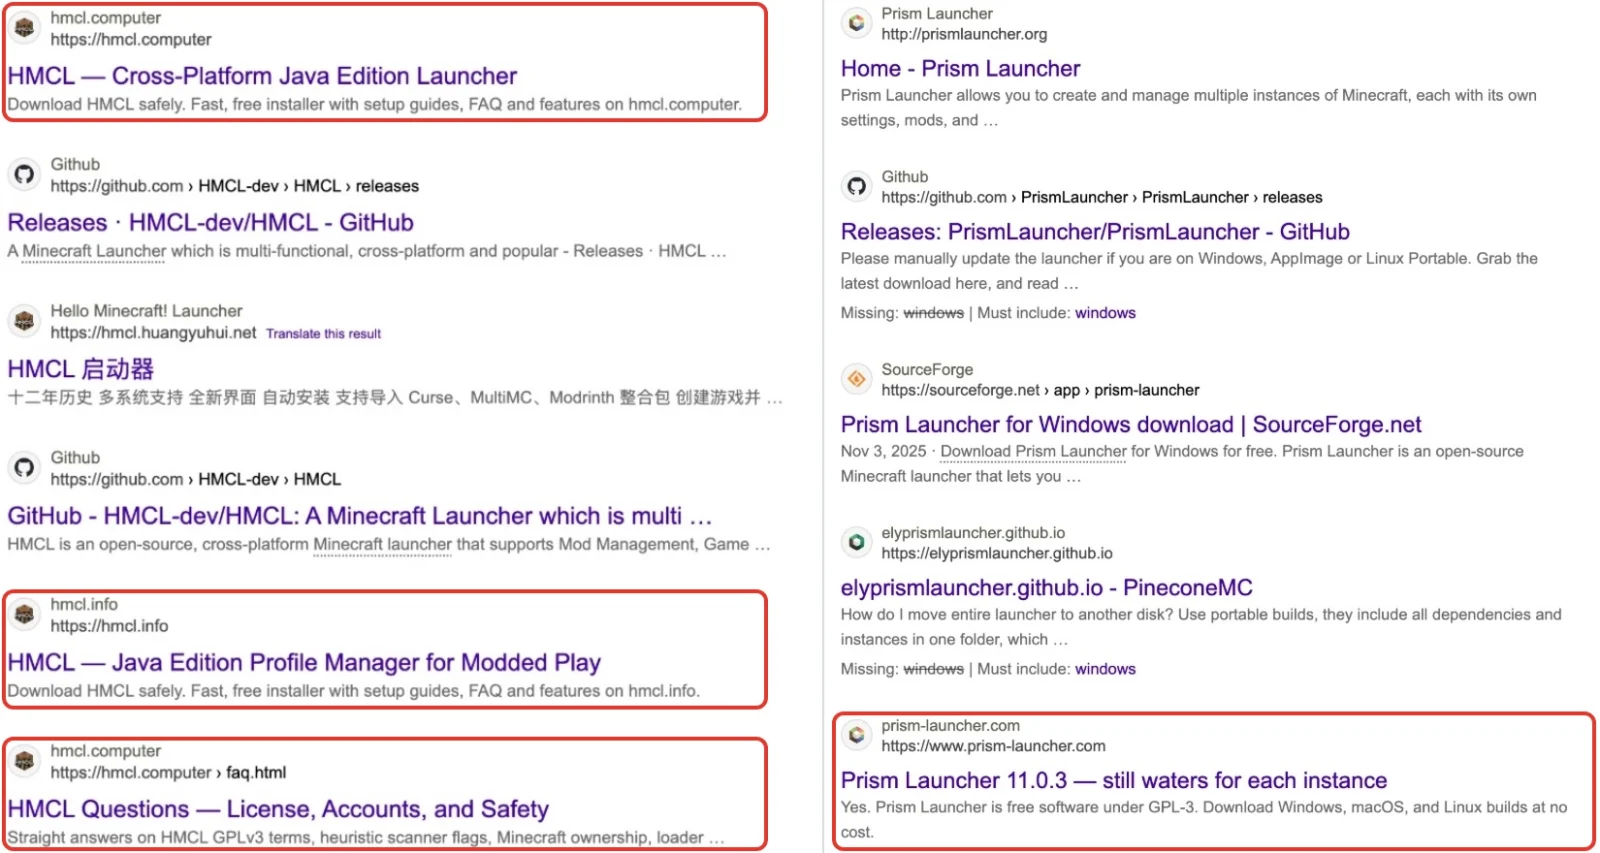
The download is a zip that looks normal. Inside, a folder named redist holds what claims to be a Microsoft Visual C++ Redistributable. It is actually ScreenConnect, a legitimate remote-support tool, set up to run as a hidden SYSTEM service that connects to the attacker. Once it is running, someone else can use your PC as if they were sitting at it.
The domains ModGrade listed: minecraftlauncher.net, minecraftlauncher.pro, minecraftlauncher.io, minecraft-launcher.app, prism-launcher.com, prism-launcher.org, prismlauncher.app, prismlauncher.io, prismlauncher.pro, prismlauncher.cc, hmcl.info and hmcl.computer. The only real homes are minecraft.net, prismlauncher.org and hmcl.huangyuhui.net.
What you should do now
If you run a server
- Open your
plugins/folder and compare every jar against the list above. Pay extra attention to anything named LagFixer that did not come from lajczi’s official pages. - For every plugin, ask: where did this file come from, and does that page still exist? A plugin whose project page has vanished is a red flag.
- Watch outbound traffic. A “metrics” request going anywhere other than bstats.org is not metrics.
- If you find one: stop the server, delete the jar, and rotate everything the server could see. That means database, RCON and panel passwords, plus any API keys in plugin configs. Then rebuild from a clean backup if you can.
- Run plugins on a host account that cannot reach anything else. Our MiniMessage exploit explainer shows how fast one weak plugin becomes a whole-server problem.
If you downloaded a launcher from a search result
- Check Task Manager for
ScreenConnect.ClientService.exe. - In Windows’ installed apps, look for a Visual C++ Redistributable entry with no version number and no Modify option.
- If you find either: disconnect from the internet, change your Microsoft, Discord and email passwords from another device, back up your files, and reset Windows. ModGrade recommends a full reset because a remote session can leave other things behind.
- Reinstall only from minecraft.net, prismlauncher.org or hmcl.huangyuhui.net, and type the address yourself instead of clicking an ad or a search result.
If you play with mods
- Remove Full Bright, MoreArmor/Weapons and any copy of Ultimate Hypixel Package 1.8.9.
- If you ran them, log out of Discord everywhere and change your password, then sign out of all Minecraft sessions from your Microsoft account.
- Expect fake “verify your account” messages next. Our Discord scams guide covers the usual follow-up tricks.
Why this keeps happening
CurseForge and Modrinth both scan uploads, and most of these projects were taken down within days of being reported. But removal only stops new downloads. A jar that is already in your server folder or modpack keeps running until you delete it, and modpacks can keep a removed mod alive for weeks. The fake launcher sites show the other half of the problem: search rankings are not proof of anything, and attackers now copy real projects down to the screenshots and FAQ.
The safe habit is boring and it works: get plugins and mods from their official project pages, keep a list of where every file came from, and never trust a launcher you did not get from its own website.
Sources 8
- ModGrade: 12 fake Minecraft launcher sites install hidden remote access on Windows PCs (Nov 5)
- ModGrade: We found malware in 34 Minecraft projects that were still online (Oct 27)
- ModGrade: Six Modrinth mods installed a password-stealing browser extension (Oct 27)
- ModGrade: LagFixer (anti lag and anti grief)
- ModGrade: Mace Smp
- ModGrade: Vaults and StaffModeration
- ModGrade: Ultimate Hypixel Package 1.8.9
- ModGrade: all malware reports